How to Structure a Corporate Social Media Policy in 2026
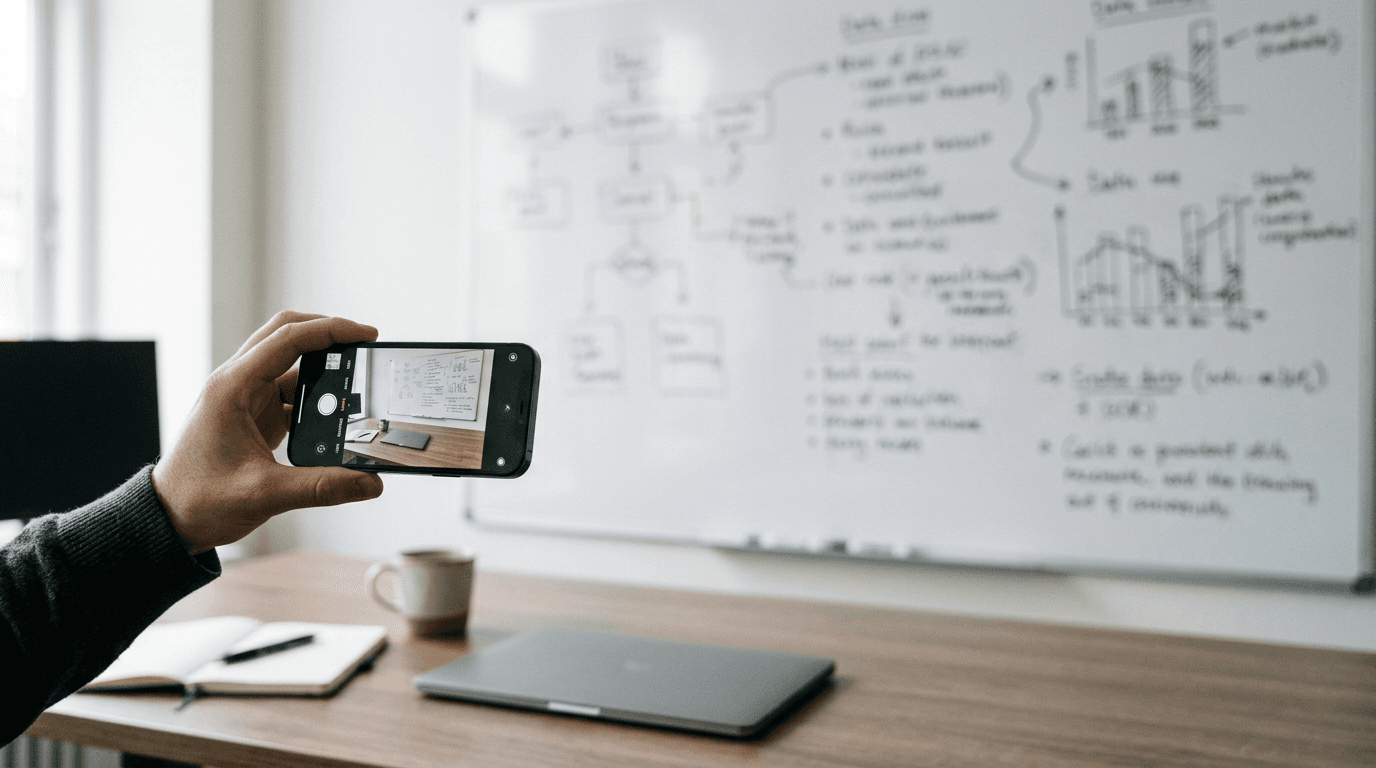
An employee posts a seemingly harmless behind-the-scenes photo from the office, accidentally capturing a whiteboard detailing an unreleased product in the background. By the time the communications team notices, the image has been screenshotted and shared across industry forums. This is the exact scenario a robust corporate social media policy is designed to prevent. It moves the organisation away from relying on common sense and establishes concrete boundaries for public communications.
Quick Summary
A corporate social media policy is a formal governance document that dictates how employees and official representatives conduct themselves on public digital platforms. It protects the organisation from reputational damage, secures digital assets, and ensures a unified public voice.
- Defines clear boundaries between personal and professional social media use.
- Standardises access control to prevent unauthorised posts and account takeovers.
- Provides an escalation matrix for rapid incident response.
- Enforces visual and tonal consistency across all regional and departmental accounts.
Table of Contents
- 1. Define the Scope and Acceptable Use
- 2. Establish Brand Voice and Visual Standards
- 3. Outline Security Protocols and Access Control
- 4. Create an Incident Response Plan
- Common Pitfalls & Troubleshooting
- FAQ
- Recommended Reads
1. Define the Scope and Acceptable Use

Where personal and professional boundaries blur
The foundation of any governance document is its scope. A policy must explicitly state who it applies to, covering full-time employees, contractors, agency partners, and temporary staff. It must differentiate between rules for managing official corporate accounts and guidelines for employees posting on their personal profiles about the company.
The mechanics involve drafting specific clauses that prohibit the sharing of confidential information, financial data, and unreleased product details. It must also address the use of company email addresses to register for personal social accounts, which creates ownership disputes if the employee leaves.
Practical rule: Never use the phrase "use common sense" in a governance document; list the exact types of information that are forbidden from public disclosure.
The mistake organisations make here is assuming employees know what constitutes confidential information. A developer might think a snippet of code is harmless to share on a personal blog, not realising it exposes a proprietary algorithm. You must provide concrete social media policy examples within the document, showing exactly what a violation looks like in practice.
2. Establish Brand Voice and Visual Standards
Why visual consistency prevents rogue campaigns
Corporate accounts often fragment when different departments or regional offices take control of their own feeds. Without strict parameters, the UK team might use a formal, corporate tone while the US team adopts a casual, meme-heavy approach. This dilutes the brand and confuses the audience.
To enforce social media branding, the policy must link directly to the company's central asset library. It should dictate the exact hex codes, typography, and logo variations permitted for public use. You must provide brand guidelines examples that show approved post templates alongside rejected, off-brand attempts. This removes subjective design decisions from the hands of social media managers.
The failure mode here is giving local teams too much creative freedom without a review process. When a regional office decides to launch a spontaneous campaign using unapproved graphics, it undermines the central marketing strategy. The fix is mandating the use of pre-approved templates for all routine communications.
3. Outline Security Protocols and Access Control
How credential management stops account takeovers
Security is the most critical, yet frequently overlooked, component of social media governance. Accounts are often created by junior staff members using generic passwords, which are then shared via unencrypted spreadsheets. When that staff member leaves, the company loses access to the account, or worse, a disgruntled former employee retains control.
The mechanics of securing accounts require implementing a centralised password manager or Single Sign-On (SSO) solution. The policy must state that no individual should know the native password for any corporate social account. Access must be granted and revoked through a central administrative dashboard. Furthermore, Two-Factor Authentication (2FA) must be mandatory, tied to a corporate device or a shared authentication app, never to an individual's personal mobile number.
The mistake people actually make is tying the 2FA recovery codes to a single person's inbox. If that person is on annual leave during a lockout, the entire communications team is paralysed. Recovery codes must be stored in a secure, shared vault accessible only to senior IT and communications directors.
4. Create an Incident Response Plan
What to do when a crisis hits the timeline
When a PR crisis occurs, the timeline moves faster than a traditional corporate approval process. If a negative story breaks or an offensive comment is accidentally posted from a corporate account, the team cannot wait 24 hours for legal to approve a response.
The policy must include an escalation matrix. This matrix defines what constitutes a minor issue (e.g., a customer complaint about a delayed delivery) versus a critical crisis (e.g., an accusation of corporate fraud). It must provide pre-approved holding statements that the social media team is authorised to publish immediately while senior management convenes.
The common failure is a complete freeze. Teams terrified of making a mistake say nothing at all, allowing public speculation to fill the void. The policy must empower the shift manager to pause all scheduled promotional posts immediately and issue a standard acknowledgement statement without waiting for executive sign-off.
Common Pitfalls & Troubleshooting
Symptom: Employees repeatedly violate the policy by posting photos of internal meetings. Diagnosis: The policy is buried in a 50-page onboarding handbook that nobody reads after their first day. Fix: Extract the key personal use rules into a one-page summary. Require annual re-certification and integrate brief, scenario-based training into regular departmental meetings.
Symptom: Regional accounts are publishing contradictory messaging on the same day. Diagnosis: There is no central visibility or shared content calendar. Fix: Revoke native posting rights. Route all regional content through a unified social media management platform where a central editor must approve posts before they go live.
Symptom: The company is locked out of its main account after a social media manager resigns. Diagnosis: The account was registered to a personal email address or a mobile number that left with the employee. Fix: Mandate that all accounts are registered to a shared alias (e.g., social@company.com) controlled by IT, and immediately reset all access tokens through the central password manager during the offboarding process.
FAQ
Can a company legally restrict what employees post on their personal accounts?
Organisations cannot police lawful private behaviour, but they can enforce policies that prohibit employees from sharing confidential corporate information, harassing colleagues online, or claiming to speak on behalf of the business without authorisation.
How often should the policy be updated?
Digital platforms and communication trends shift rapidly. The policy should be audited annually to account for new platforms, updated security protocols, and shifts in employment law.
Who should be responsible for enforcing the policy?
Enforcement is a cross-departmental responsibility. Human Resources handles employee conduct violations, IT manages access control and security breaches, and Corporate Communications oversees brand alignment and public messaging.
Should we list every social network in the document?
No. Naming specific platforms guarantees the document will be outdated within months. Frame the rules around "public digital communications and social networking platforms" so the governance applies regardless of which app is currently popular.